Your Firewall Already Saw the Attack: Bringing AI Detection to Network Logs
How we’re extending Logster’s AI threat detection from endpoints to firewalls and NetFlow, with explained verdicts and endpoint-to-network incident linking.
Logster v1.3.0: Whitelisting You Can Trust, Evidence You Can Click
Logster v1.3.0 rebuilds whitelisting so approvals can’t be abused, links every verdict to the evidence behind it, and adds storage-aware retention.
Whitelisting a Graph Is Harder Than Whitelisting a Filename
What we learned building a way for analysts to approve a pattern of behaviour rather than a filename — two definitions of “the same”, why matching has to be cheap, and the bug that made approvals silently stop working.
What Alert Fatigue Actually Costs You
Alert fatigue is discussed as a morale problem. It is a budget problem. A model you can run on your own figures — triage time, tuning debt, attrition and dwell time.
12 Questions That Actually Separate Threat Detection Vendors
Every vendor says the same words, so the burden falls on the questions you ask. Twelve that genuinely discriminate — including the ones we find uncomfortable.
You Can’t Just Paste Logs Into an LLM
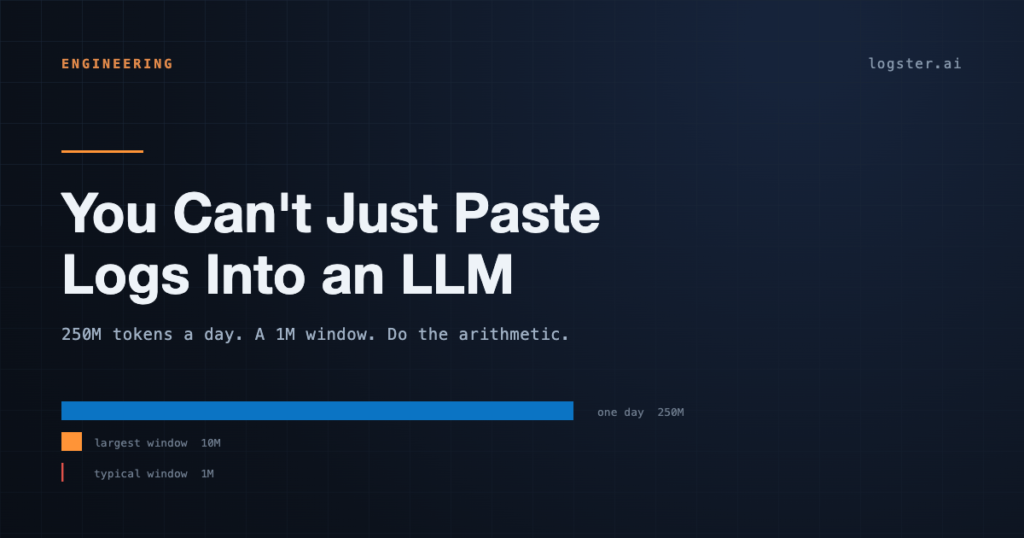
The first idea everyone has is to point a language model at their logs. It demos beautifully and falls apart on arithmetic. A look at why — and why the model was never the hard part.
Process Ancestry Lies to You: Reading Parent-Child Relationships Without Getting Fooled
Parent-child process relationships are the backbone of behavioural detection — and they break in more ways than most detection engineers expect. A practical guide to PID reuse, PPID spoofing, orphan reparenting, and what to do about each.